
Multiply your detection team
Autonomous threat research, hunting and detection engineering
Built around how security teams operate. AI that knows your environment, your detections, and your preferences. Automatically investigates relevant threats, hunts for evidence of impact, checks your coverage, and builds detections for what’s missing. Give your team more time to act, with the tools to manage, govern and scale the work.
Three problems Enterprise closes.
Agents that hunt and engineer for you.
Nightwatch picks up new intel as it publishes, decides whether it applies to your environment, and hunts your telemetry for it. Findings and draft detections are waiting when you get in.
Every answer shows its work: the intel it came from, the queries it ran, the coverage it compared against. You get hunt results and ready made detections.
Tune and manage what you already run.
Ask where your gaps are for ClickFix and get an answer grounded in your library and your environment, not a generic feed.
Scheduled audits surface stale rules, duplicate coverage, and missing documentation, and suggest the tuning. Generate a report for leadership in one click.
Detection as code, deployed to the systems you already run.
Read from and write back into Google SecOps, Microsoft Sentinel, SentinelOne, Splunk, and GitHub. Version it, review it, audit the drift.
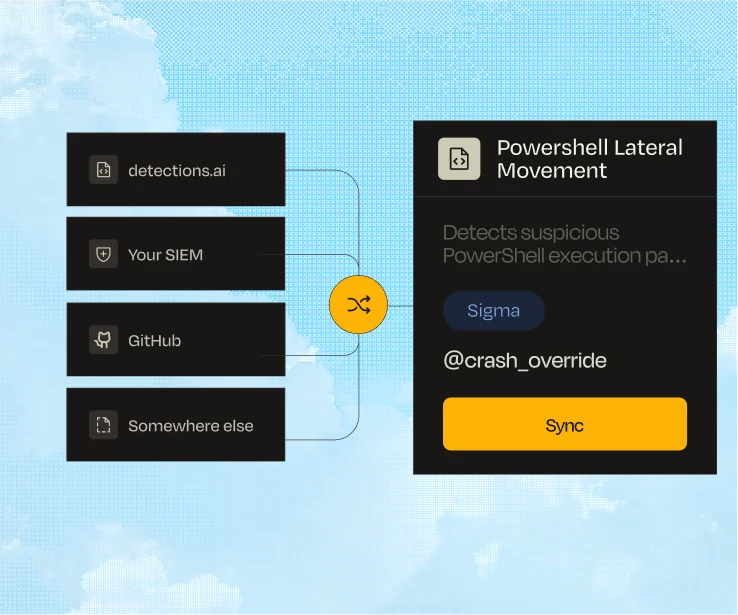
Pull from any source, deploy to any destination, in one place. SAML SSO, REST API, and an MCP server make it work the way a security org already operates.
AI that works your library, your intel, and your stack.
Nightwatch
New intel publishes around the clock. Nightwatch baselines your environment, identifies what matters to you, hunts for evidence of impact, checks your library for coverage, and drafts detections for what’s missing. It does the work automatically, updates its memory as it learns, and shows you how it reached its findings.
AI Librarian
Answer any question about your detection library. "Where are our gaps for Salt Typhoon?" "Which of our SPL rules cover lateral movement?" "Show me everything that mentions CVE-2026-48282." Get an answer grounded in your detections, not the public ones.
Bulk AI operations
Apply translation, tuning, or audits across your entire library in one pass. Migrate a few hundred Sigma rules to KQL. Re-tune everything tagged Defense Evasion. Run an audit against your last quarter of intel.
A platform shaped to how security teams actually work.
One workspace for how detection teams operate — organize, sync, deploy, and automate.
Your detections may live in detections.ai, in your SIEM, in GitHub, or somewhere else. Enterprise keeps them in sync. Pull from any source, deploy to any destination, audit drift in one place.
Bring detection engineering to your team.
Get a real reply from a real person.